GRC-as-a-Service pairs our risk analysts with a compliance automation platform: policies managed, evidence collected continuously, controls mapped once across every framework you carry — and an analyst who turns it all into insight your board can act on.
The frameworks keep multiplying — SOC 2, HIPAA, CMMC, ISO 27001, the cyber-insurance questionnaire — and each one asks for the same evidence in a different shape. Spreadsheets and screenshot folders burn your best people's hours and go stale the day the auditor leaves. GRC-as-a-Service makes compliance continuous: the platform does the mundane collection, our analysts connect the dots, and the same work that satisfies the auditor tells you where your real risk lives.
We map your environment — people, technology, data, obligations — tune audit-ready policy templates to how you actually operate, connect your cloud and identity stack, and crosswalk your controls to every framework you carry.
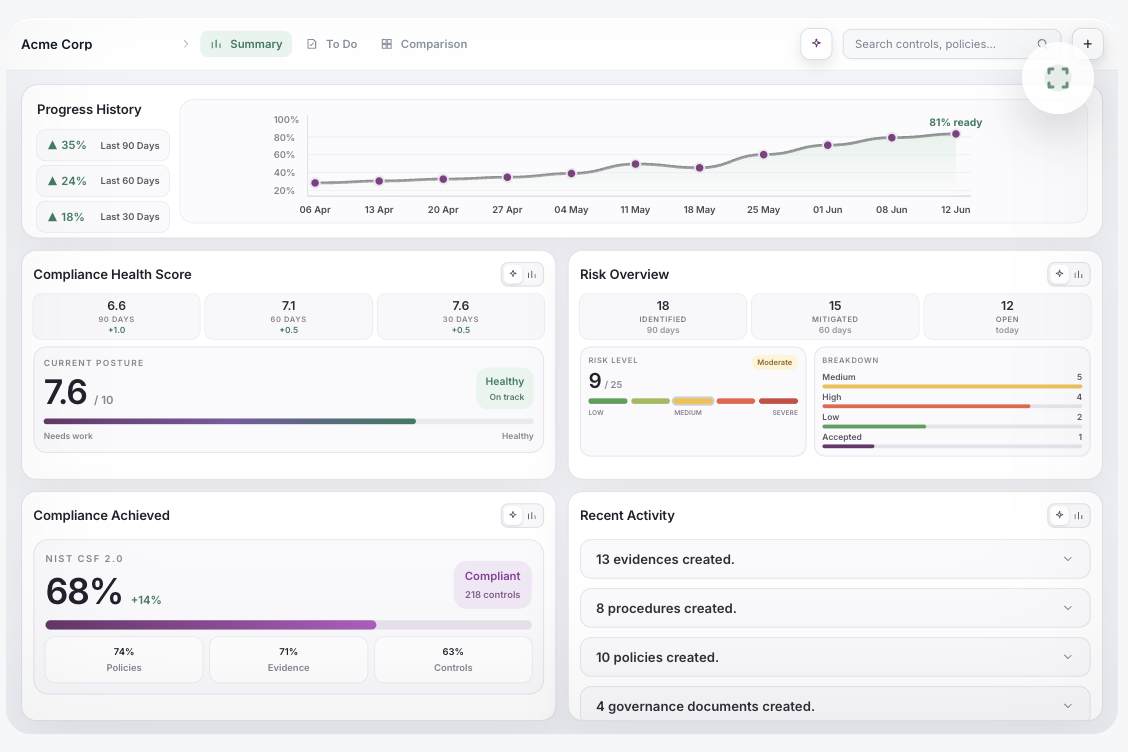
Integrations pull evidence continuously, controls are monitored around the clock, and policy acknowledgements are tracked automatically. Our analysts review the posture on a set cadence and keep your risk register current — you see health, not homework.
When the auditor, the customer, or the board asks, the answer already exists: audit-ready evidence packages, a customer-facing trust portal, and a compliance brief your executives can read in five minutes.
Everything routine is automated; everything that requires judgment gets a named C3 analyst who knows your business. One managed service, four fronts.
A library of audit-ready policy templates tuned to your organization, mapped to your control set, with acknowledgement tracking and an annual review cycle that actually happens.
Direct integrations with your cloud, identity, and security tools collect evidence continuously and monitor control health — so audit prep stops being an annual archaeology dig.
A living risk register maintained by our analysts, seeded from real findings, plus third-party risk assessments of the vendors who hold your data — reviewed on a cadence, not when something breaks.
Audit-ready evidence packages, auditor collaboration led by C3, and a customer-facing trust portal that answers security questionnaires before they're sent.
Every plan is fully managed and includes the platform, the integrations, and a named C3 analyst. Pricing scales with the frameworks you carry and the evidence scope, not the size of your team.
For organizations getting their first framework done right — and done once.
For organizations carrying multiple frameworks that want compliance to run continuously.
For audited, regulated, or customer-scrutinized organizations that need an embedded GRC function.
Pricing scales with the number of frameworks and the scope of evidence we manage. Book a scoping call and we'll scope the right plan and give you a real number.
Cream City Cyber is honored to stand among the businesses powering Milwaukee's growth — proof that world-class security expertise and deep community roots belong together.