We benchmark your security program against the frameworks that matter — NIST CSF 2.0, CIS Controls, ISO 27001 — score the maturity of every capability, and hand you a board-ready roadmap that says where to invest first, and why.
Security budgets get approved when leadership can see the gap. Self-assessments overrate maturity, auditors and insurers ask "against what standard?", and every executive team eventually asks the same question: are we spending on the right things? A disciplined benchmark replaces "we think we're fine" with a scored, evidence-based picture of where you stand — and a sequenced plan for where the next dollar should go.
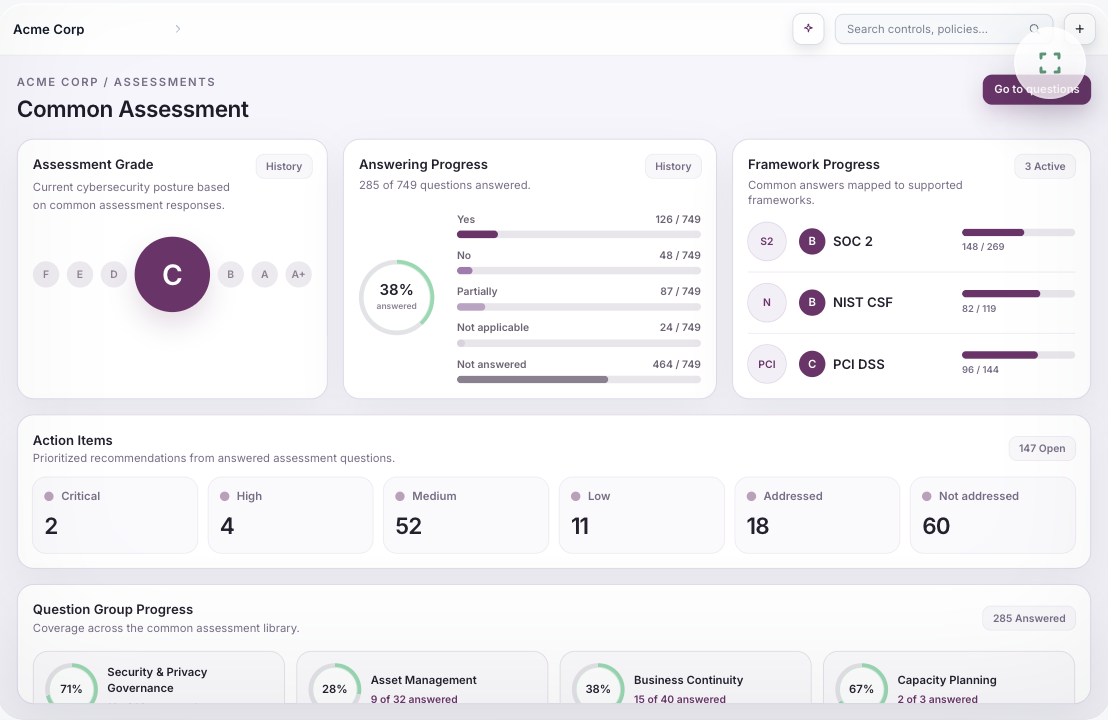
Structured interviews and evidence sampling across your environment — people, technology, data, and vendors — against the framework you choose. Every answer is scored consistently, so the result is defensible, not a vibe.
Capability-level maturity scoring against NIST CSF 2.0, CIS Controls v8.1, ISO 27001:2022, or the framework your industry demands — crosswalked so one assessment answers many obligations, with gaps ranked by risk and cost to close.
A board-ready findings briefing and a prioritized, sequenced roadmap that connects every recommended investment to the risk it retires — where to focus, where to invest, and what to defer with eyes open.
The assessment is built to be reused: score once, and map the result to every framework, auditor, insurer, and customer questionnaire that asks.
NIST CSF 2.0, CIS Controls v8.1, ISO 27001:2022, CMMC, and regulatory overlays for healthcare, finance, and manufacturing — benchmarked against current versions, not last decade's.
Consistent, capability-level scoring across your program with a compliance-health view — so you can compare domains, defend the number, and measure movement between assessments.
Answer once, map everywhere. One assessment populates every framework you carry today and shortens the path to the ones you'll carry next — no duplicate interviews, no repeated homework.
A prioritized improvement roadmap with owners and sequence, plus a seeded risk register your team — or our GRC-as-a-Service program — can operate from day one.
Every assessment is analyst-led and ends in a briefing, not a binder. Pricing scales with the frameworks in scope and the depth of evidence validation, not the size of your team.
For organizations that need a credible first read on where the program stands.
For organizations carrying multiple obligations that want one defensible answer.
For organizations that want maturity managed as a number, not revisited as a project.
Pricing scales with the frameworks in scope and the depth of evidence validation. Book a scoping call and we'll scope the right assessment and give you a real number.
Cream City Cyber is honored to stand among the businesses powering Milwaukee's growth — proof that world-class security expertise and deep community roots belong together.